
QR codes have become ubiquitous in our daily lives since the pandemic. Restaurants, transport, payments, authentication: these little black and white squares make many interactions much easier. However, this growing popularity has also attracted a new type of threat: the malicious QR code, also known as “quishing”.
What exactly is quishing?
Quishing, a contraction of “QR” and “phishing”, is an evolution of phishing techniques. Unlike classic phishing, which mainly relies on fraudulent emails containing suspicious links, quishing uses malicious QR codes to send victims to booby-trapped websites or trigger actions on their devices.
This technique exploits the natural trust users place in QR codes. They are generally seen as practical, secure tools, which makes victims less suspicious when they scan them. Cybercriminals take advantage of this perception to hide their malicious intentions behind a seemingly harmless interface.
Quishing relies on the fact that users cannot visually decipher the content of a QR code. With a classic link, the URL is visible and can raise suspicion, especially thanks to awareness campaigns at school or at work. A malicious QR code, on the other hand, perfectly hides its final destination, only revealing its true purpose once it has been scanned.
It is impossible to tell a safe QR code from a malicious one with the naked eye.
Understanding how a QR code works
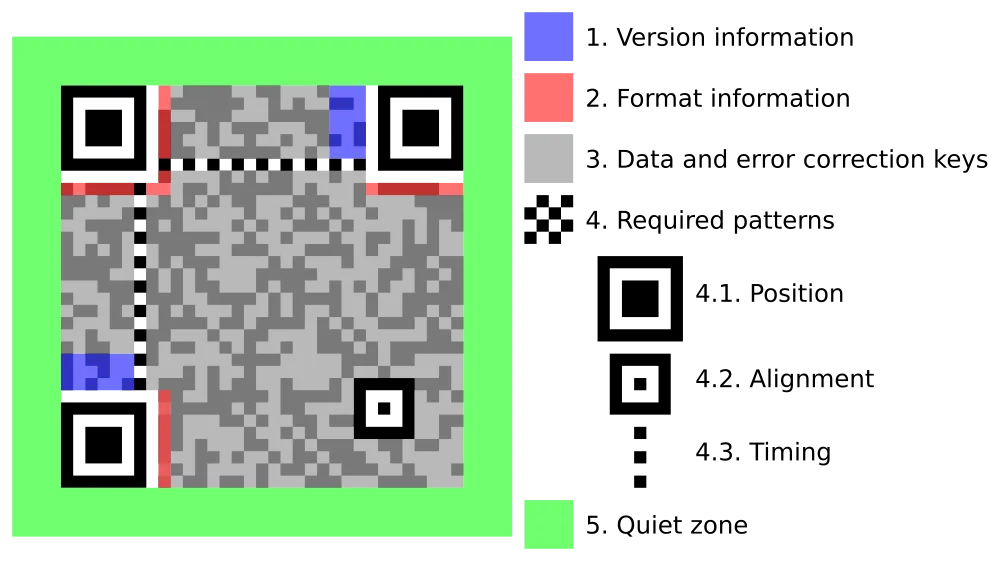
Before looking at the malicious side, it helps to understand the basic mechanism of legitimate QR codes. A QR code, short for “Quick Response code”, is essentially a two-dimensional matrix capable of storing various kinds of information as black and white geometric patterns.
Technically, a QR code works like an advanced barcode that can hold up to 4,296 alphanumeric characters. Unlike traditional barcodes, which only store numbers, QR codes can encode URLs, text, phone numbers, email addresses or even Wi-Fi login details. This versatility explains their massive adoption across many sectors.
Source
When you scan a QR code with your smartphone, the camera captures the image of the code and an app instantly decodes the geometric patterns to extract the encoded information. The process relies on error-correction algorithms, so the code still works even when it is partly damaged or dirty, another major advantage.
The security of a legitimate QR code depends on the trust placed in the source that generated and distributed it. An official restaurant, a public administration or a well-known company has no interest in creating malicious codes. This natural trust relationship is precisely the weakness cybercriminals exploit in their quishing attacks.
How does a malicious QR code work technically?
Creating a malicious QR code is a relatively simple process, which partly explains why this threat is proliferating. Attackers start by creating a fraudulent website or setting up a malicious server to host their booby-trapped content. The site may imitate a legitimate service such as a bank, a social network or an e-commerce platform. This step is similar to phishing.
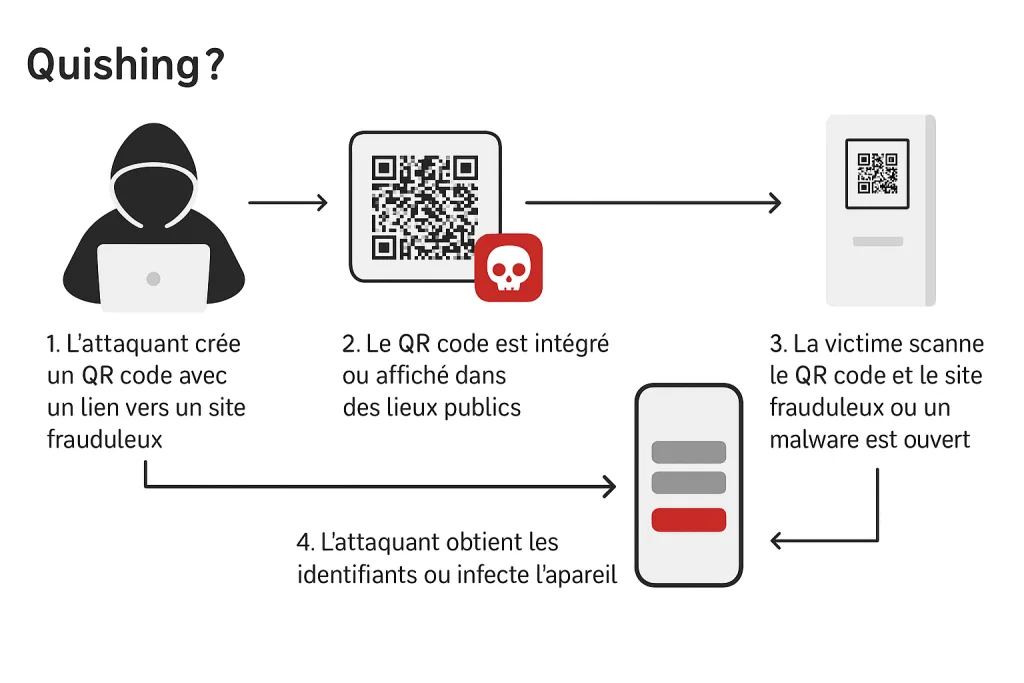
Once the fraudulent site is in place, the cybercriminals generate a QR code pointing to this malicious destination using free online tools. These QR code generators do not check what the code points to, so malicious codes can be created without restriction.
The next step is to distribute these malicious QR codes in places where they will go unnoticed. Attackers can print them on fake flyers, stick them over existing legitimate QR codes, or spread them through channels such as social networks or messaging apps.
When a victim scans the malicious QR code, several scenarios can unfold depending on the attacker’s intentions. The code can redirect to a fake website with a form to steal credentials, trigger the automatic download of a malicious app, or initiate a call or text message to a premium-rate number, depending on the operating system.
The different types of malicious QR code attacks
Quishing comes in several variants, each suited to specific goals.
Personal data
The most common remains credential theft through redirection to fake login pages. In this case, the user who scans the malicious QR code is sent to a site that perfectly imitates the interface of a popular service such as Gmail, Facebook or their online banking.
In July 2024, Netskope Threat Labs observed a 2,000% increase in traffic to phishing pages delivered via Microsoft Sway, mainly targeting Microsoft 365 credentials.
Native features
Another particularly insidious variant exploits smartphones’ native features. Some malicious QR codes can automatically trigger actions such as sending emails, dialling phone numbers or adding contacts to the address book. Although these actions seem harmless, they can be used to confirm that a phone number or email address is valid for later spam campaigns. Cybercriminals also use QR codes to distribute malicious apps.
Cryptocurrencies
More recently, cases of quishing exploiting cryptocurrencies have been observed. Attackers create fake QR codes for digital wallet addresses, diverting transactions to their own accounts. This technique mainly targets users of Bitcoin ATMs or attendees of crypto-related events.
Recognising the signs of a malicious QR code
Identifying a malicious QR code before scanning it is a real challenge, but several indicators can raise your suspicions. The context in which you come across the QR code is the first thing to consider:
- Be wary of codes stuck over other materials, especially on official posters, restaurant menus or public information boards.
- The location of the QR code can also reveal malicious intent. Codes placed in busy places such as public transport or shopping centres, with no obvious commercial or informational context, should put you on alert.
- Likewise, QR codes received by email or via social networks from unknown senders carry a high risk.
- In September 2024, Sophos employees were targeted by spear-phishing emails containing QR codes in PDF attachments, a perfect illustration of how sophisticated these attacks are becoming.
- The visual quality of the material can also be a clue. Poor-quality stickers, blurry prints or codes visibly stuck over other elements often suggest fraudulent tampering.
Some QR code reader apps display the destination URL before redirecting you. Use this feature to examine the web address. Suspicious URLs often contain spelling mistakes, unusual domain extensions or URL shorteners that hide the real destination.
Checking the URL is sometimes not enough. A particularly insidious variant uses Microsoft Sway to host phishing pages that look legitimate. Attackers exploit the legitimate “sway.cloud.microsoft” domain to distribute valid URLs pointing to pages hosted on Microsoft’s official service, making detection extremely difficult.
Some quishing campaigns use Cloudflare Turnstile as an extra layer of protection against static website scanners, preventing their domains from getting a bad reputation.
Good practices to protect yourself from quishing
Protection against quishing mainly relies on adopting good practices when using QR codes. The first rule is to be careful and think before scanning any QR code you come across. Always ask yourself whether the code is legitimate and whether it makes sense to scan it in the context where you found it.
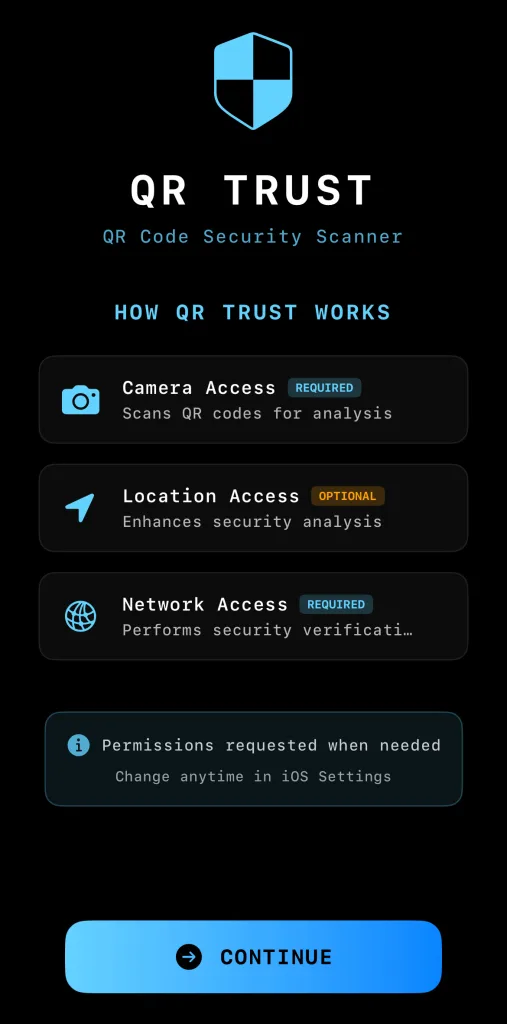
Dedicated apps can also help, for example QR Trust from Qerberos. I actually had the chance to meet its founder, Angus Chen, during a trip to Estonia for the 2025 edition of CyberWizards.
He explains why he created the app:
My mother fell victim of cyber crime. Our family suffered mentally, physically and financially. Seniors are among the most vulnerable populations in society. I felt the need to fight QR code phishing that has become a global problem – Angus Chen
Using this type of app is very simple:
- Download the app; for QR Trust, it is on the App Store.
- Allow access to the camera and network (required). You can also allow access to your location for correlation.
- That’s it, time for your first scan!
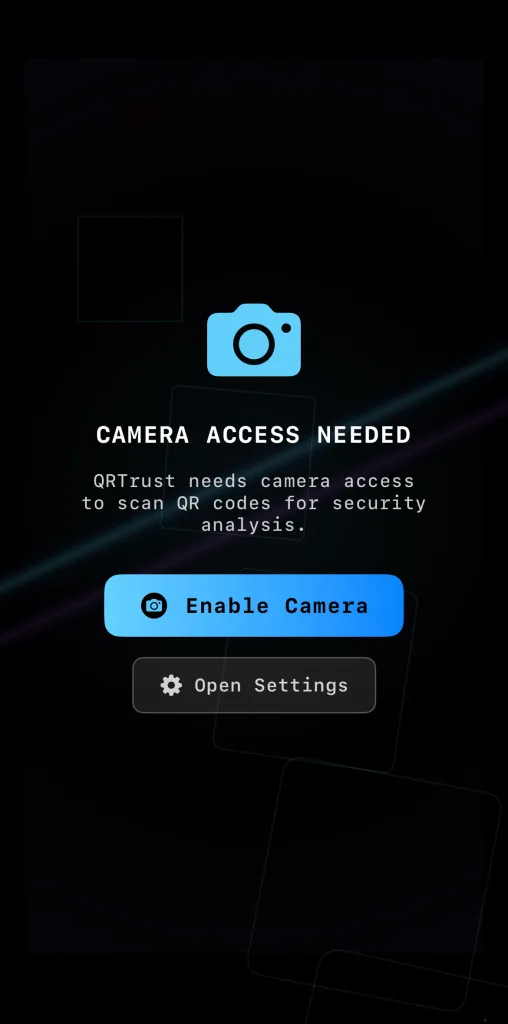
When you scan, you can get three types of results:
- Safe
- Unknown
- Threat detected
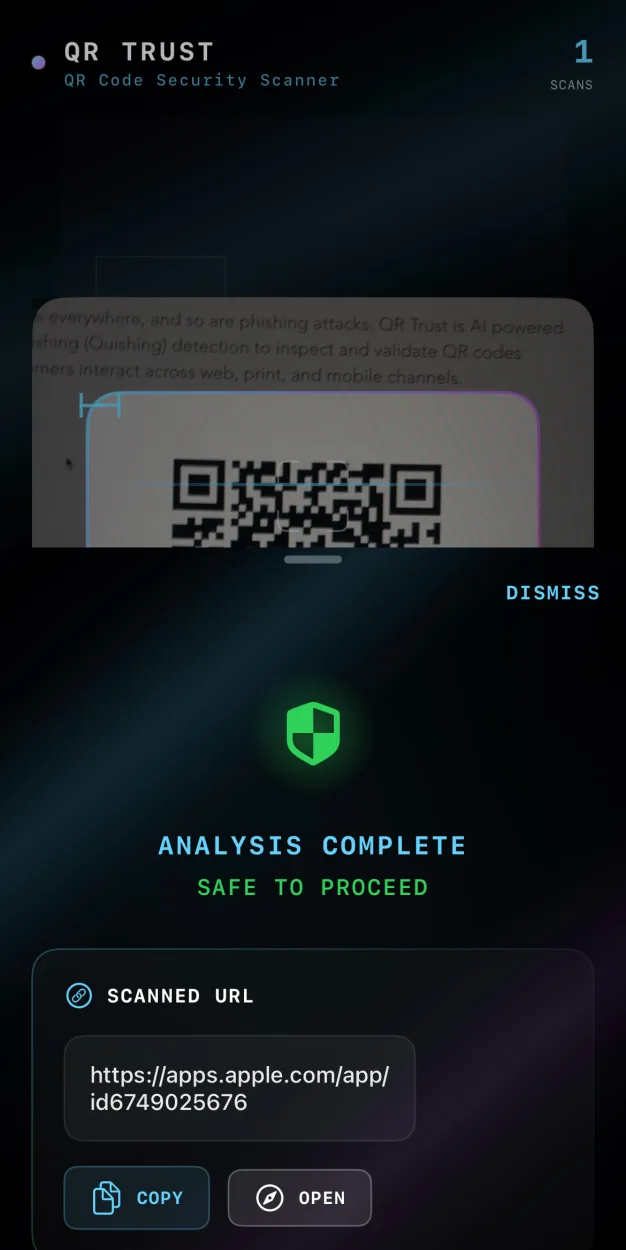
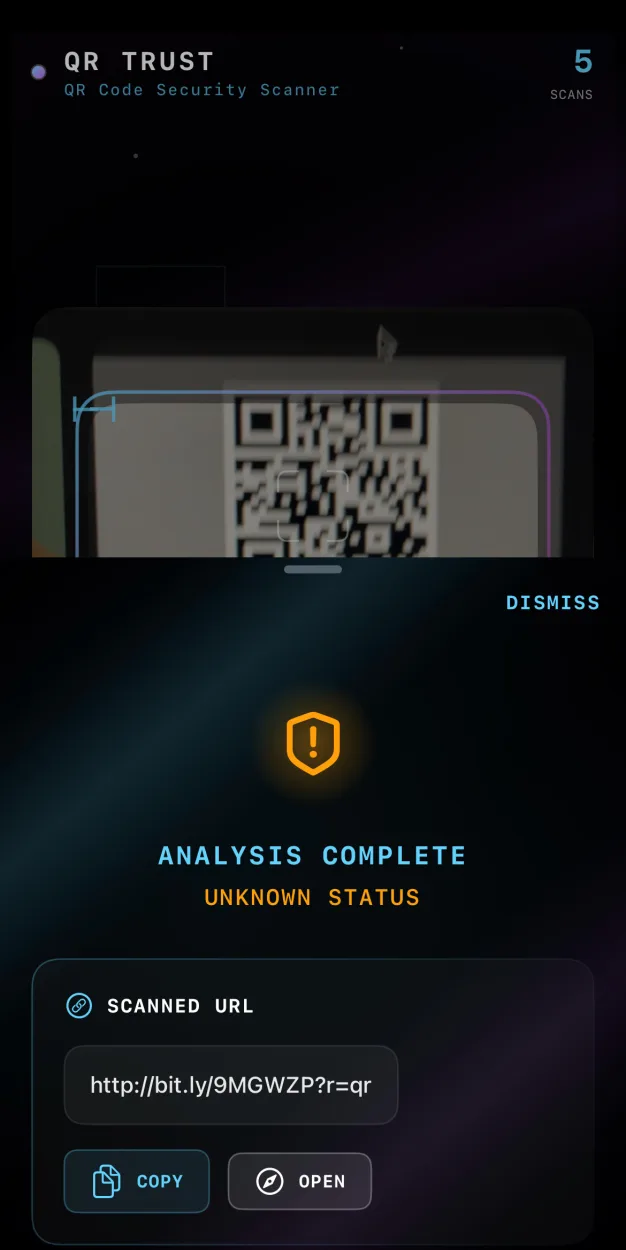
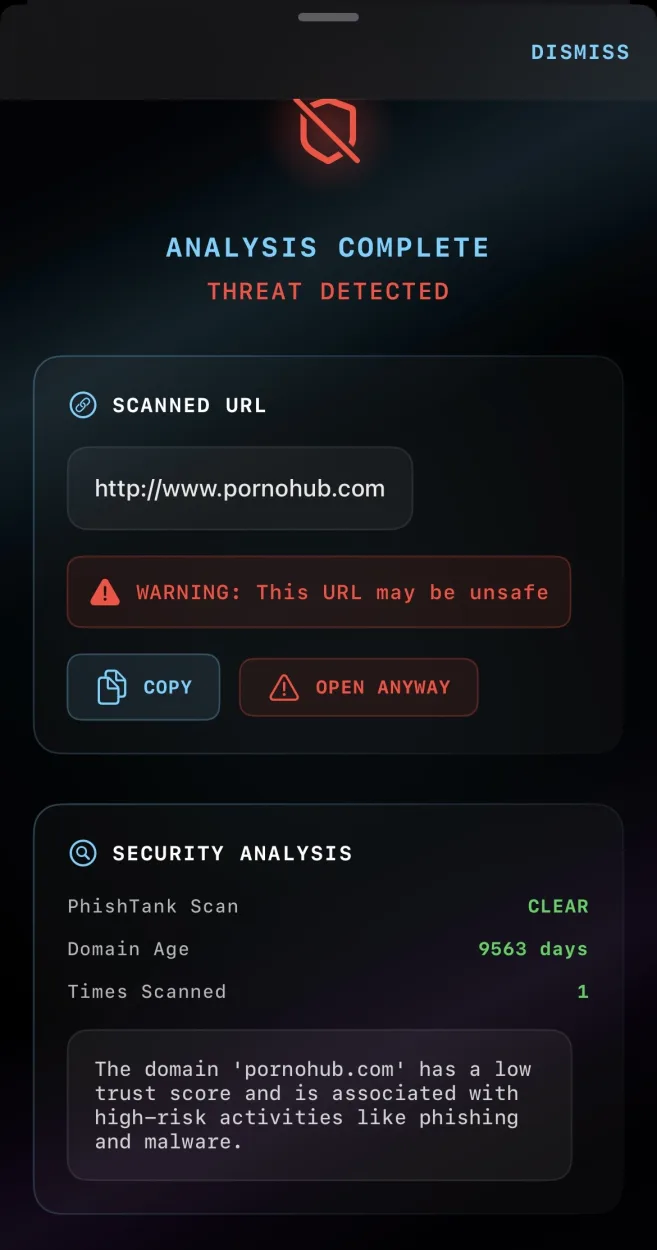
Use specialised apps
Prefer QR code reader apps that display the destination URL before redirecting you. This feature, available in many specialised apps, lets you examine the destination and spot any anomalies before you continue.
Be careful with your information
Avoid entering sensitive information on websites reached through QR codes, especially login credentials, banking details or personal data. If you really need to access a service, go directly to the official site by typing the URL into your browser.
Keep everything up to date
Keep your apps and operating system up to date. Security updates regularly fix vulnerabilities that could be exploited by malicious QR codes redirecting to sites designed to compromise your device.
How quishing is evolving and future trends
Quishing keeps evolving as cybercriminals refine their techniques and adapt to new technologies. The growing integration of QR codes into our consumer habits, accelerated after the pandemic, gives attackers an ever-expanding playground. Electric vehicle charging stations are also contributing to this expansion.
The emergence of new technologies such as augmented reality and contactless payments also opens new attack vectors for quishing. Cybercriminals are starting to exploit these innovations to create deceptive user experiences, maliciously blending the physical and digital worlds.
In response to this growing threat, the industry is developing increasingly sophisticated protection solutions. Automatic detection of malicious QR codes is starting to be built in natively, providing a first line of defence against these attacks.
What to do if you fall for a malicious QR code
If you suspect you have fallen victim to a malicious QR code attack, reacting quickly is crucial to limit the potential damage. Your first action should be to disconnect your device from the internet immediately to stop any communication with the attackers’ servers.
If you entered login credentials on a fraudulent site, change all the passwords concerned immediately, starting with the most sensitive accounts such as your email, banking services and social networks. Also enable two-factor authentication on all your important accounts if you haven’t already.
If the attack led to a suspicious app being installed, uninstall it immediately and run a full scan of your device with reputable antivirus software. Don’t hesitate to call in an IT security professional if you notice persistent abnormal behaviour.
Report the incident to the relevant authorities, for example the Cybermalveillance.gouv.fr platform in France, which collects and processes reports of cyberattacks. Reporting helps feed threat databases and can help identify ongoing attack campaigns.
Malicious QR codes: frequently asked questions
A malicious QR code is a QR code created by cybercriminals to redirect users to fraudulent sites, install malware or steal personal information as part of quishing attacks.
Signs of a dangerous QR code include suspicious placement (stuck over another code), an unusual context, poor print quality, a dubious origin (unsolicited email, social networks) and an unofficial URL, although you need a compatible app to see it.
Yes, quishing can cause real damage: credential theft, malware installation, financial fraud or identity theft. How discreet the attack is makes it particularly effective.
Use a QR reader app that shows the URL before redirecting, avoid scanning suspicious codes, never enter sensitive information via a QR code and keep your devices up to date.
Disconnect your device from the internet immediately, change your important passwords, uninstall any suspicious app, scan your device with an antivirus and report the incident to your security team if it happened at work. In a personal context, file a complaint if things escalate.

Leave a Reply