
On 26 November 2025, OpenAI notified its users of a security incident involving Mixpanel, its web analytics provider. The intrusion, detected on 9 November 2025, led to the exfiltration of limited analytics data about API accounts on platform.openai.com. Users of ChatGPT and other OpenAI products are not affected by this Mixpanel data breach.
What happened in the Mixpanel data breach
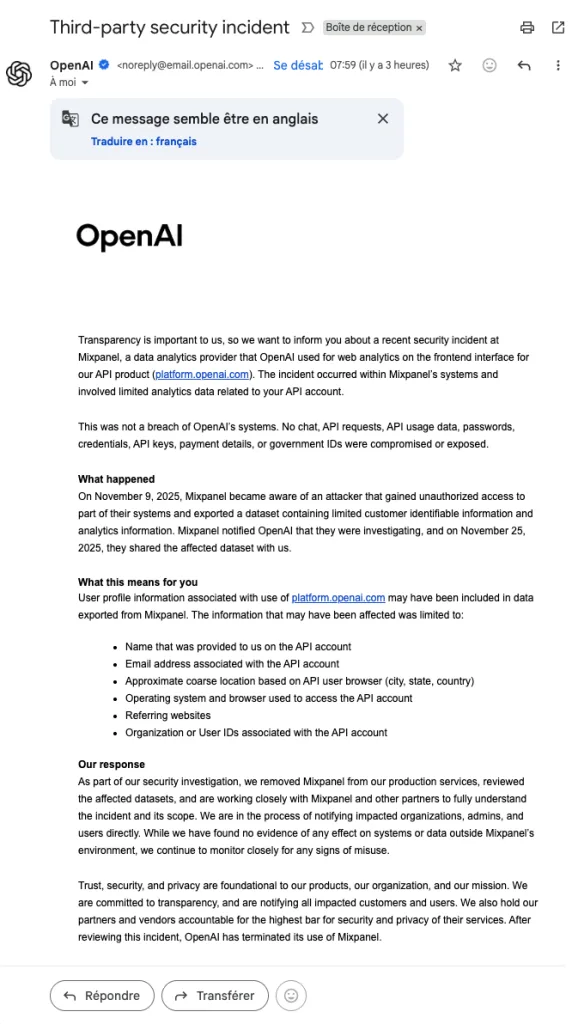
On 9 November 2025, Mixpanel found that an attacker had gained unauthorised access to part of its systems and exported a dataset containing identifiable customer information and analytics data. Mixpanel informed OpenAI of its investigation and shared the affected dataset on 25 November 2025.
OpenAI responded quickly by removing Mixpanel from its production services and analysing the affected datasets. The company stresses that its own infrastructure was not compromised. No conversations, API requests, API usage data, passwords, credentials, API keys, payment details or government ID documents were compromised or exposed.
What data was exposed in the Mixpanel breach
The data exported from the Mixpanel environment included limited user profile and analytics information related to the use of the platform.openai.com interface. The potentially affected information is limited to the following:
The name provided on the API account, the email address associated with the API account, approximate browser-based location (city, state, country), the operating system and browser used to access the API account, referring websites, and the organisation or user IDs linked to the API account.
This Mixpanel data breach only concerns metadata collected for analytics purposes on OpenAI’s API platform. Technical usage data, prompts, generated responses and sensitive information remain untouched.
OpenAI’s response to the Mixpanel data breach
After reviewing the incident, OpenAI stopped using Mixpanel. The company is notifying affected organisations, administrators and users directly by email. OpenAI says it found no evidence of impact on systems or data outside the Mixpanel environment, but continues to actively monitor for any sign of misuse.
Beyond Mixpanel, OpenAI is conducting additional, broader security reviews across its vendor ecosystem and raising security requirements for all partners and providers. This is part of a wider effort to strengthen third-party risk management.
Risks associated with the Mixpanel data breach
OpenAI warns that the exposed information, which includes names, email addresses and API metadata, could potentially be used in phishing or social engineering campaigns targeting users or their organisations.
The company recommends that API users stay alert to suspicious communications. Treat unexpected emails or messages with caution, especially those containing links or attachments. Check that any message claiming to come from OpenAI is actually sent from an official OpenAI domain. OpenAI never asks for passwords, API keys or verification codes by email, text message or chat.
OpenAI encourages users to strengthen account security by enabling multi-factor authentication. The company does not recommend resetting passwords or rotating API keys, since the breach did not compromise them.
Questions about how analytics data is handled
This Mixpanel data breach raises questions about data-sharing practices with third-party providers. According to the Cybernews research team, sending non-anonymised, identifiable user data was a choice made by OpenAI. Technical commentators argue that OpenAI could have avoided passing personally identifiable information to its reporting system, a practice that runs against security best practices.
The situation illustrates the challenges of digital supply chain security. Even when a company maintains high security standards on its own systems, vulnerabilities at third-party providers can expose customer data. The Mixpanel data breach shows the need for stronger due diligence when selecting and monitoring external vendors.
Affected users can contact OpenAI’s team at mixpanelincident@openai.com with any questions or for assistance. The company has committed to providing updates if new information emerges from ongoing investigations.
Frequently asked questions
The Mixpanel data breach is a security incident that occurred on 9 November 2025, in which an attacker exported a dataset from Mixpanel’s systems, exposing limited analytics information about OpenAI API users.
The exposed data includes names, email addresses, approximate locations, operating systems, browsers, referring websites and organisation or user IDs of OpenAI API accounts. No conversations, API keys, passwords or payment information were compromised.
No, only users of the OpenAI API via platform.openai.com are potentially affected. Users of ChatGPT and other OpenAI products are not impacted by this breach.
OpenAI is notifying all affected users, organisations and administrators directly by email. If you use the OpenAI API and haven’t received a notification, you are probably not affected.
No, OpenAI does not recommend resetting passwords or rotating API keys, as these were not compromised in this data breach.
OpenAI immediately removed Mixpanel from its production services, ended its relationship with the provider, launched broader security reviews across its entire vendor ecosystem and strengthened security requirements for all third-party providers.
The exposed information could be used for targeted phishing or social engineering campaigns. Stay alert to suspicious communications and never share passwords, API keys or verification codes by email, text message or chat.
No, the incident occurred in Mixpanel’s systems and did not involve unauthorised access to OpenAI’s infrastructure. It is the compromise of a third-party provider used for web analytics.

Leave a Reply