
On Tuesday 14 May, Google released emergency patches for a high-severity 0-day flaw tracked as CVE-2024-4761. Google also announced that the vulnerability is being actively exploited.
An out-of-bounds write bug in the V8 engine
The vulnerability was reported anonymously on 9 May 2024 and no further details have been disclosed. It affects the V8 JavaScript and WebAssembly engine.
This type of bug can enable several things: writing to memory areas outside the intended ranges, data corruption or even arbitrary code execution. The CVE has a CVSS v3 base score of 8.8/10.
Google says it is aware that an exploit exists in the wild, all the more reason to apply the patches.
The company says it does not want to share further information about the attack so as not to increase its scale.
Protecting yourself from CVE-2024-4761
Simply update Chrome to version 124.0.6367.207/.208 for Mac and Windows and version 124.0.6367.207 for Linux-based distributions.
The update will roll out gradually over the coming days or weeks. The full list of changes in this version is available in the changelog.
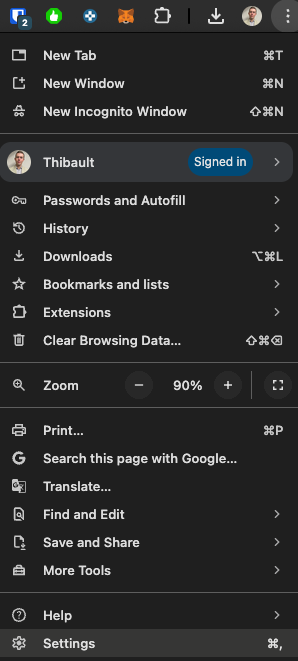
If you don’t want to wait for the automatic update, you can force it by going to Settings and then About Chrome.
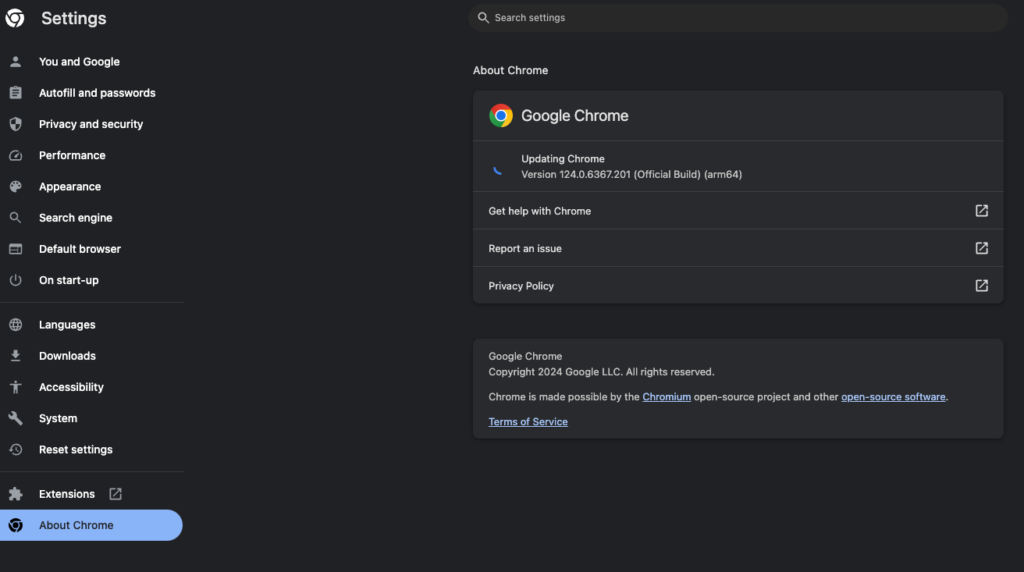
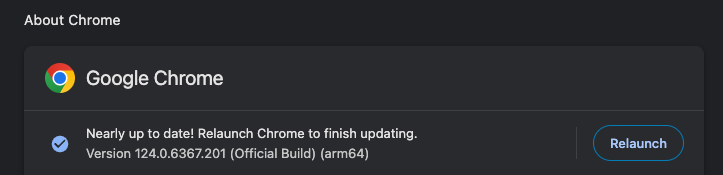
Then simply relaunch Chrome to apply the patch.
Google keeps piling up CVEs
2024 is a tough year for the American giant, which keeps racking up CVEs from these “anonymous pentesters“ affecting Chrome:
- CVE-2024-0519: CVSS 8.8: out-of-bounds memory access in V8 in Google Chrome prior to 120.0.6099.224 allowed a remote attacker to potentially exploit heap corruption via a crafted HTML page.
- CVE-2024-2886: 8.8: a use-after-free vulnerability in the WebCodecs API, used by web applications to encode and decode audio and video.
And others:
- CVE-2024-2887
- CVE-2024-3159

Leave a Reply