
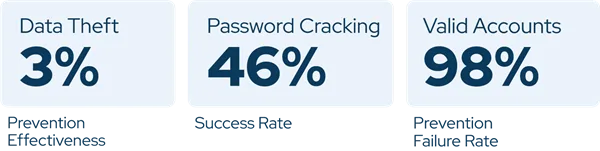
The latest Blue Report 2025 reveals an alarming decline in password security in businesses. Based on more than 160 million attack simulations run in real production environments, the report shows that 46% of the environments tested had at least one password cracked successfully, double the 25% recorded in 2024.
The explosion of password-related vulnerabilities
This spectacular 84% increase in a single year illustrates how deficient password policies persist in businesses. Picus Security data, collected between January and June 2025, shows that organisations continue to underestimate the importance of robust password policies despite constantly evolving attack techniques.
Dr Süleyman Ozarslan highlights this worrying reality, stressing that organisations must assume adversaries already have access to their systems. This “assume breach” approach becomes crucial as passwords are increasingly easy to compromise.
Stolen credentials that are almost impossible to stop
Beyond password cracking, the report reveals that attacks using valid credentials succeed in 98% of cases. This statistic shows how formidably effective the MITRE ATT&CK T1078 (Valid Accounts) technique is, allowing cybercriminals to bypass defences using compromised legitimate accounts.
The situation is made worse by the prevalence of infostealer malware, which has tripled, making mass credential theft easier. Once they have valid passwords, attackers can move laterally through systems without triggering alerts, making them extremely hard to detect.
The collapse of overall security defences
The report also highlights a general decline in the effectiveness of cybersecurity defences. The attack prevention rate fell from 69% in 2024 to 62% in 2025. Even more worrying, only 3% of data exfiltration attempts were blocked, compared with 9% the previous year.
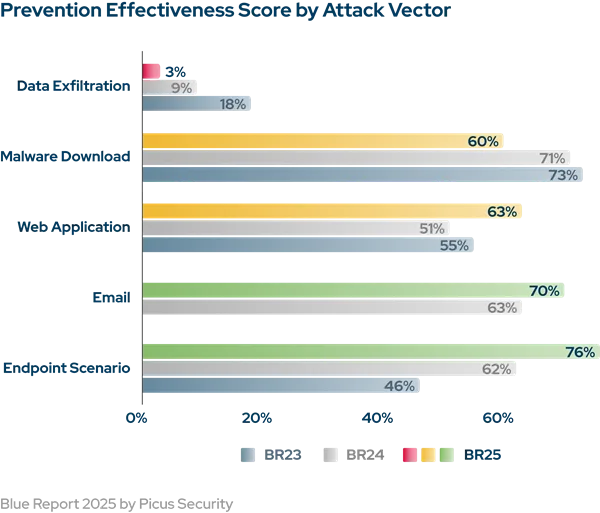
These figures show that even when passwords are compromised, organisations struggle to detect and stop the malicious activity that follows. Only 14% of attacks trigger alerts, leaving most intrusions unnoticed.
Solutions to secure business passwords
In this critical situation, several measures are needed to strengthen password security. Deploying password managers is an essential first step, making it possible to generate and store complex, unique passwords for each service.
Multi-factor authentication (MFA) is an essential extra layer of security, even if the main password is compromised. Organisations should also review their password policies to require stronger complexity criteria and regular renewal.
Employee training remains crucial to raise awareness of the risks of weak passwords and of the social engineering techniques used to steal them.
An absolute cybersecurity emergency
The Blue Report 2025 data is a wake-up call for every business. With password-related vulnerabilities doubling in a single year, adopting password management solutions is no longer optional but an absolute necessity to maintain an acceptable level of security.
Business passwords: frequently asked questions
The evolution of cracking techniques, the rise of infostealer malware and outdated password policies that are still in place explain this decline.
A tool that automatically generates, stores and manages complex, unique passwords for all your accounts.
No, it must be combined with strong passwords and user awareness for optimal security.
Choose well-known, end-to-end encrypted solutions with regular security audits and secure sharing features.

Leave a Reply